
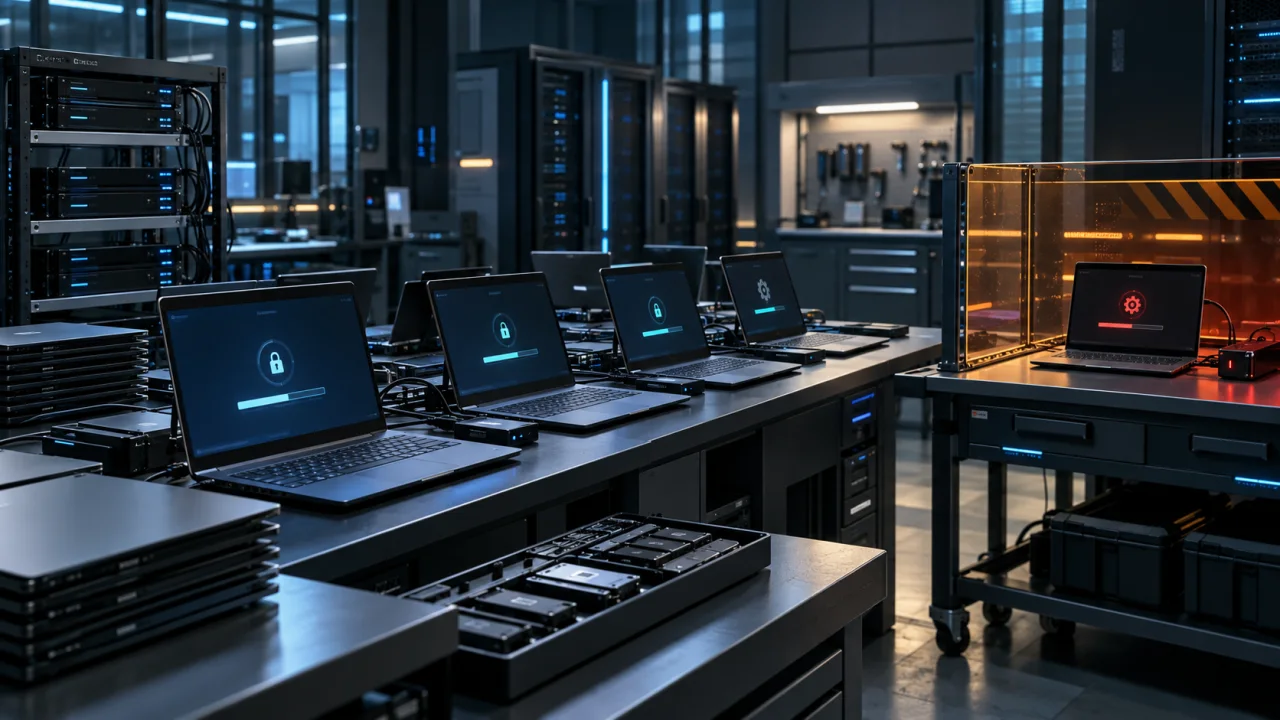
Define the supported endpoint population
A baseline needs a known scope: operating systems, device ownership, user roles and applications. Separate ordinary workstations, privileged devices, shared terminals and specialist systems because one configuration may create different operational consequences. Unsupported devices should be visible and placed on a retirement or isolation plan.
Begin with high-value outcomes: timely updates, disk encryption, secure boot, managed security tooling, restricted local administration, controlled applications and reliable logging. Record the source and version of each requirement so future platform changes can be evaluated deliberately.
Deploy through rings and evidence
Test changes with representative devices and users before broad enforcement. Use deployment rings, health checks and rollback criteria. A successful configuration command is not proof of effective coverage; collect state from the endpoint and investigate devices that stop reporting.
Make exceptions specific to an application or workflow, not a permanent exemption from management. Give them owners and review dates. Where a control creates repeated failure, fix the design or dependency rather than teaching users to bypass it.
Operate the baseline as a product
Assign ownership for requirements, deployment tooling, support and security evidence. Review drift, failed updates, inactive agents and unsupported versions. Keep incident responders able to isolate a device and preserve evidence without depending on the affected user account.
Reassess the baseline after major platform releases, incidents and business change. Useful measures include managed coverage, encryption and update health, local administrator reduction, drift age and time to isolate. Tie metrics to action thresholds rather than dashboard decoration.
What to do next.
- ✓Separate standard, privileged and specialist device profiles.
- ✓Define versioned security outcomes and evidence.
- ✓Use representative pilot and deployment rings.
- ✓Investigate devices that stop reporting.
- ✓Give exceptions owners and expiry dates.
- ✓Measure drift, support status and isolation readiness.
Use guidance responsibly
Technology, provider behaviour and legal requirements change. Validate implementation details against current official documentation, test changes safely and obtain qualified legal advice where required.
Sipho Williams
Microsoft Security ContributorCovers identity, collaboration security and privileged administration across modern Microsoft environments.
More from this writer